Introduction
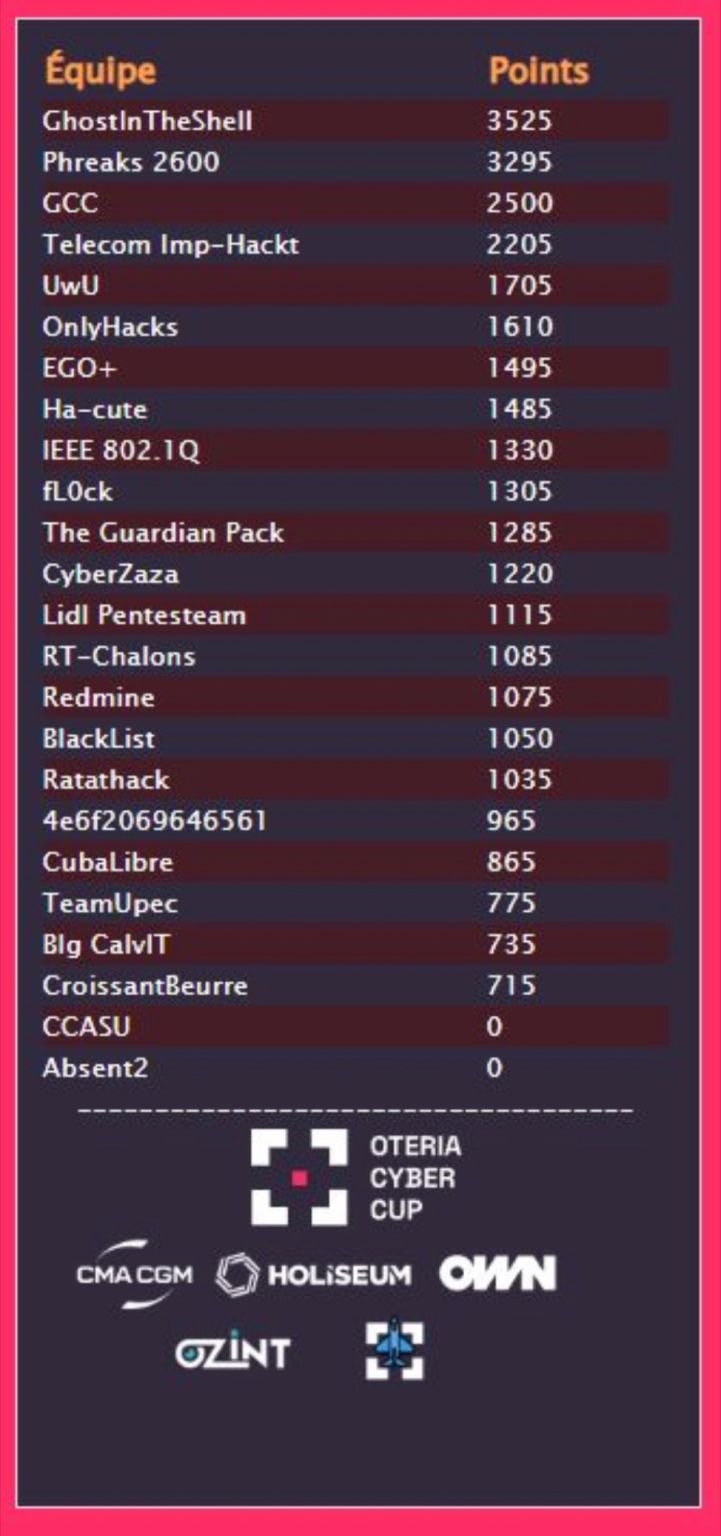
In the vast landscape of cybersecurity, events like Capture The Flag (CTF) competitions serve as immersive experiences for enthusiasts keen on honing their skills. The Oteria Cyber Cup, an annual event orchestrated by Oteria, a distinguished cybersecurity school based in Paris, unfolded on December 16, 2023. This event spanned a day, bringing together a diverse array of cybersecurity aficionados ready to immerse themselves in the complexities of Maritime Advanced Persistent Threats (APTs), with over 2,500€ in cash prizes.
https://www.youtube.com/watch?v=oKg8GN9lWkU
Oteria in details
At the heart of this cyber spectacle is Oteria, an educational institution located in Gennevilliers, Paris. Renowned for its five-year curriculum, Oteria molds cybersecurity professionals by offering a three-year Bachelor’s degree followed by a two-year Master of Science in Cybersecurity. The faculty, comprising recognized experts such as Rémi Gascou (PODALIRIUS) as coach of the CTF team, and Julien Métayer in OSINT, employs a dual-competence pedagogy, aligning students with the dynamic demands of the cybersecurity industry.
Diving into the Event
Having participated in the Oteria Cyber Cup as a conceptor, my experience was nothing short of exhilarating. The ambiance at the event was vibrant, blending a sense of camaraderie among participants with the intellectual rigor of the challenges. A seven-hour marathon ensued, with 25 teams, each consisting of 4 to 5 members, navigating through challenges tailored for various skill levels—beginner, intermediate, and advanced. The sponsors were DGSE and CMA-CGM, the presence of companies like CMA-CGM, a global leader in logistics, showcased the industry’s acknowledgment of the importance of nurturing cybersecurity talent. Here are the entities behind each challenges:
 CMA CGM proposed a challenge about spoofing maritime GPS coordinates
 OWN has produced a forensic exercise that puts players in the shoes of a DFIR analyst.
 Without any surprise, OZINT produced an OSINT challenge
 Holiseum has produced a software radio exercise.
 Rafale 101 is made up of Oteria students, and produced web exploitation, pwn and OSINT challenges.
Forensic challenge
As working for OWN, it was assigned to me, to carry out the forensic challenge, which was the largest of all the event’s challenges.
First of all, my colleague Marion Lachiver and i worked on the challenge scenario, producing several reports for the client in order to get feedback on the progress and direction of our work, as a reminder, it had to be on the subject of APT in the maritime sector. We got into the game and added a lot of lore and history, while making sure it remained coherent and preserving the technical aspects of the challenge. The challenge emulates an incident response to the compromise of an SME by an advanced attacker, several advanced techniques of initial access, persistence and evasion have been used. The analyst will be asked to understand each and every technique used in order to reconstruct the picture of past events.
Once the scenario was complete, I started its technical realization, working in a VM to simulate the victim’s machine and producing a lot of noise (navigation and legitimate use of the device) before, during and after the compromise. The aim of producing so much noise was to complicate the analyst’s task and ensure that this challenge was as close as possible to the real thing and to what you might see in an intervention. I then carried out the compromise by putting myself in the attacker’s shoes and using advanced methods of exploitation like initial access, evasion and persistence. Finally, I recovered the main artifacts for post-compromise investigation with a tool such as FastIR giving me a zip archive of about 4 GB ready to be distributed to players.
I thought it was a pity that this challenge got lost in time, so I’m not going to give you any more information about it in this article, so as not to spoil it for you if you want to do it on your own. Attached to this article are the investigative artifacts provided to players during the event, as well as the challenge writeup. You can then have fun reproducing the investigation at home.
To encourage you to do it at home, here are the initial instructions given to the player at the start of the challenge:
You’re an analyst in the DFIR team of a cyber-security company. Today, a maritime SME called Becolab is calling on your services following a leak of confidential data that was posted on darknet cybercriminal forums at the beginning of November 2023. After one of your colleagues analysed the company’s DNS server, everything suggests that the data leak originated from the workstation of the person in charge of human resources, who had observed some abnormal behaviour on her workstation a few days earlier but thought she had solved the problem and didn’t inform her employer. Your manager has assigned you to investigate this machine, and you are expected to reconstruct the scenario of past events, understand the initial compromise and identify what data has been extracted. Good luck!
Files of the challenge:
Conclusion
In conclusion, the Oteria Cyber Cup 2023 was a resounding success, seamlessly blending education and excitement in the realm of cybersecurity. The event not only showcased the talent and dedication of participants but also highlighted the commitment of Oteria to providing a platform for practical, hands-on learning. As I reflect on my day at the Oteria Cyber Cup, I am left with a sense of accomplishment, having navigated through the intricacies of a forensics challenge and gained valuable insights into the world of Maritime APT threats.
I’d like to end by thanking the oteria school and the people I worked with on this challenge:
Here is a post from Oteria published 4 days ago about the past event:
https://www.linkedin.com/posts/oteria-cyber-school_ctf-activity-7153294901680492546-EMDq